Home > ESG >

Risk Management

Risk Management Policies and Procedures

To strengthen corporate governance and establish sound risk management practices, the Board of Directors approved the Company's Risk Management Policy on December 16, 2020. The policy guides all business units to effectively identify, measure, monitor and control the various risks arising from their operations, and to keep those risks within an acceptable level, so as to achieve a reasonable balance between risk and return and support the Company's sustainable operation.

Scope of Risk Management

Risks involved in the Company's businesses include operational risk, market risk, financial risk, climate change and environmental risk, occupational safety risk, information security risk, and compliance risk.

Organizational Structure
Risk Management Operation Situation

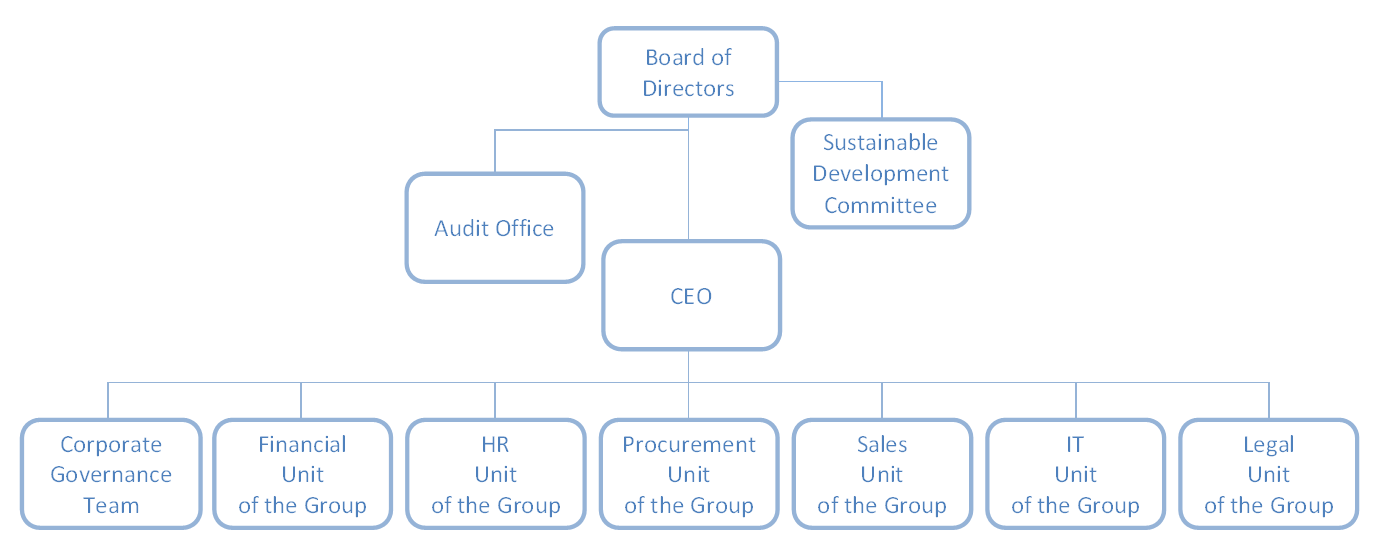
The Company began promoting its risk management mechanism in 2020 and has reported its operation to the Board of Directors once a year since that year. In 2025, the Company held a risk management meeting to identify the risks it faces, assess those risks and determine response measures, and on December 19, 2025 reported to the Sustainability and Nomination Committee and the Board of Directors on the implementation of the Company's risk management — including risk identification, assessment of risk impacts (covering sustainability issues and climate risk), and the operation of the risk management strategies adopted. Under the responsibilities approved by the Board, the Sustainability and Nomination Committee is responsible for promoting and supervising the implementation of enterprise risk management, and for submitting any necessary improvement recommendations arising from its review to the Board for further examination. The effectiveness of controls over operational-level risks is audited by the Internal Audit Office in accordance with the annual audit plan.

Materiality Assessment Process and Results

In accordance with the GRI 2021 Standards and the AA1000 Stakeholder Engagement Standard (AA1000 SES), the Company evaluated dependency, responsibility, level of concern, influence and diversity of perspectives, and identified six categories of stakeholders highly relevant to its operations. In 2025, topics of concern were collected through day-to-day communication and questionnaire surveys, with 88 valid responses received, comprising 17 suppliers, 52 employees, 11 customers, 5 representatives of financial institutions, 2 investors and 1 other respondent.

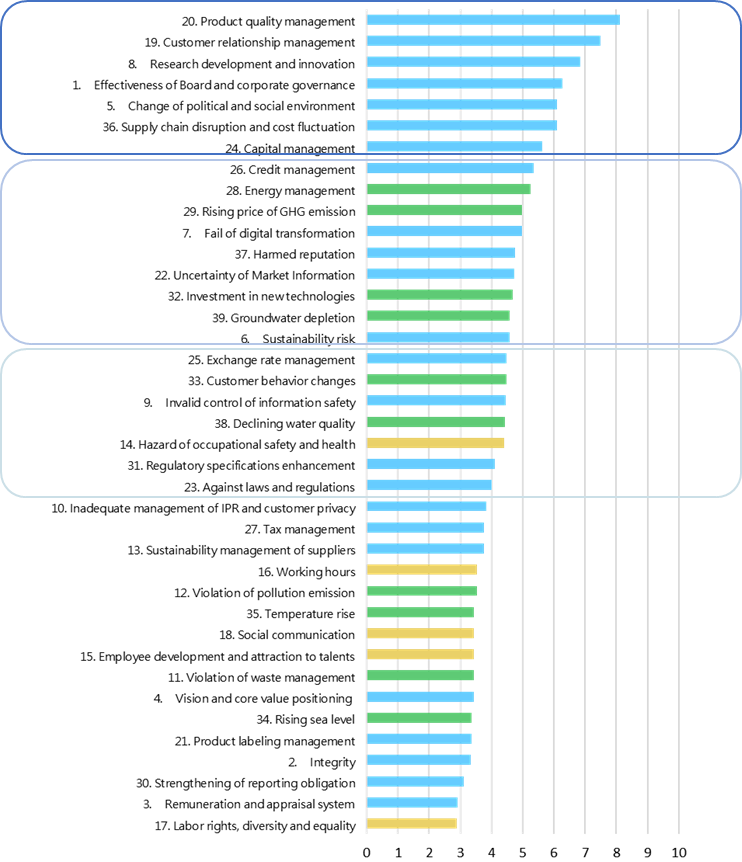
Senior management scored the significance of the impact of 40 topics on the Company's operating activities, using risk likelihood and risk impact as assessment indicators, and ranked them by the product of the two to identify material topics. A total of 13 material topics were confirmed for 2025, corresponding to 7 GRI Topic Standards and 7 self-defined topics.

Materiality Level Classification Basis (Likelihood × Impact) Number of Topics
A Highest materialityProduct of 5.5 or above7
B High materialityProduct of 4.5 or above but below 5.56
C Moderate materialityProduct of 4.0 or above but below 4.511
D Low materialityProduct below 4.016
2025 Material Topics Matrix
Comparison of Material Topics for the Most Recent Two Years
Rank 2025 Material Topics 2024 Material Topics
1Customer relationship managementProduct quality management
2Product responsibility managementCustomer relationship management
3Research and innovationResearch development and innovation
4Board governance and corporate governance effectivenessEffectiveness of Board and corporate governance
5Risks from external political and economic environment changesChange of political and social environment
6Supply chain disruptions and climate risk-induced cost variationsSupply chain disruption and cost fluctuation
7Financial risk managementCapital management
8Energy managementCredit management
9Reputation riskEnergy management
10Market and demand fluctuation risksRising price of GHG emission
11Water resource risks (water quality, quantity, and sources)Fail of digital transformation
12Carbon pricing and rising carbon cost risksHarmed reputation
13Information security managementUncertainty of market information
14Investment in new technologies
15Sustainability risk
16Groundwater depletion
For the implementation of risk management in 2025 (including sustainability issues and climate risk), please refer to the following:
Risk Management and Stakeholder Communication.pdf

Information Security Management Strategy and Structure

(I) Information Security Risk Management Framework
1. Information Security Organization
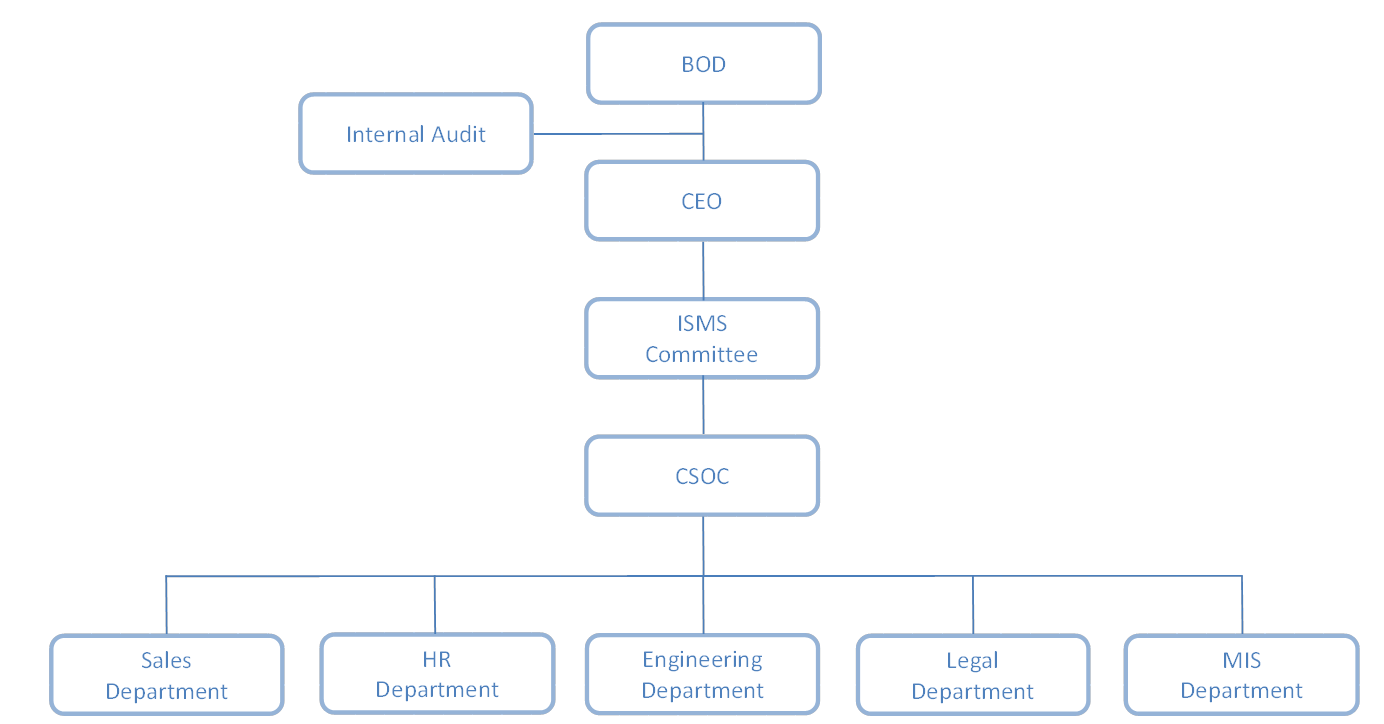
Apex Circuit (Thailand) Co., Ltd. (APT), the operating entity of the Group, established the Information Security Management System Committee (ISMS Committee) in 2022. The committee has 32 members and convened 4 meetings during 2025. The ISMS Committee governs the APT Cyber Security Operation Center (CSOC), which is responsible for coordinating the formulation, implementation, risk management and compliance review of the Group's information security and protection policies. The dedicated information security officer of the center reports annually to the parent company's Board of Directors and CEO on the effectiveness of information security management and on related issues and directions. The Group's Internal Audit Office conducts audits to ensure internal compliance with information security standards, procedures and regulations.

To implement the information security strategies set by the CSOC and ensure internal compliance with the relevant standards, procedures and regulations, the dedicated information security officer and center personnel work with the business, human resources, engineering and legal departments to review and decide on information security and information protection guidelines and policies each year, and to ensure the effectiveness of information security management measures.
2. Group ISMS Committee Organizational Structure
(II) Information Security Policy
1. Group ISMS Strategy and Structure
Information security and the protection of operational data are important cornerstones of sustainable business development and of maintaining core competitiveness. To enhance the security and stability of the Group's information and communication operations, ensure the confidentiality, integrity and availability of information assets, and support the smooth conduct of the Group's business, the Group is committed to strengthening its information security management mechanisms and defense capabilities, establishing a secure and trustworthy computing environment, and safeguarding the security of systems, data, equipment and networks so that the Company's key information assets and information systems operate normally.

To effectively implement information security management, the Group's information security organization holds regular monthly meetings through the CSOC. Following the Plan-Do-Check-Action (PDCA) management cycle, it reviews the applicability of information security policies and protection measures, and periodically reports implementation results to the ISMS Committee.
Cycle Focus Key Elements
Plan Information Security Risk Management Corporate information security; compliance with the international information security standard (ISO/IEC 27001); training employees to obtain professional competency certification
Do Multi-Layer Security Protection Network security; email gateway security; application security; data surveillance and maintenance; personnel and physical security; data security enhancement
Check Monitoring of Information Security Management Continuous information security control; information security attack simulation exercises; quantitative assessment of information security
Action Review and Continuous Improvement Review of information security measures for improvement; information security education, training and publicity
2. Concrete Management Programs
Program Measures
(1) Network Security Deploy advanced technologies for computer scanning and system and software updates.
Strengthen network firewalls and network controls to prevent viruses from spreading across machines and zones.
(2) Equipment Security Establish an incoming-equipment virus scanning mechanism to prevent machines containing malware from entering the Group.
Deploy endpoint anti-virus measures by computer type and strengthen malware behavior detection.
(3) Application Security Establish application security checklists, evaluation criteria and improvement targets for the development process.
Continuously strengthen application security controls and integrate them into the development process and platform.
(4) Enhanced Data Security Protection Develop advanced information protection tools that use data labeling to strengthen document confidentiality classification and data protection.
Apply encryption controls and effective tracking to documents and data.
Control outbound email.
(5) Education and Training Raise employee awareness of email social engineering attacks and conduct phishing defense detection.
Hold regular information security drills to strengthen employee security awareness.
(6) Cybersecurity Maturity Assessment Engage external experts, including information security audit organizations and cyber risk assessment agencies, to periodically assess the Group's network and information security.
Integrate objective third-party verification results with threat intelligence to conduct risk analysis and strengthen the information security management system.
3. Resources Invested in Information Security Management
A total of THB 6,476,000 was invested to enhance information security protection.
4. Annual Management Targets and Achievement
Management Target 2025 Achievement
Maintain ISO 27001 certification statusCertified to ISO/IEC 27001:2022 (valid 2023.08.27–2026.08.26)
100% information security protection coverage100%
100% completion rate for information security training and NDA signing100%
Incidents of customer privacy infringement or loss of customer dataNone occurred in 2025
5. Training and Information Security Policy Communication
Item 2022 2023 2024 2025
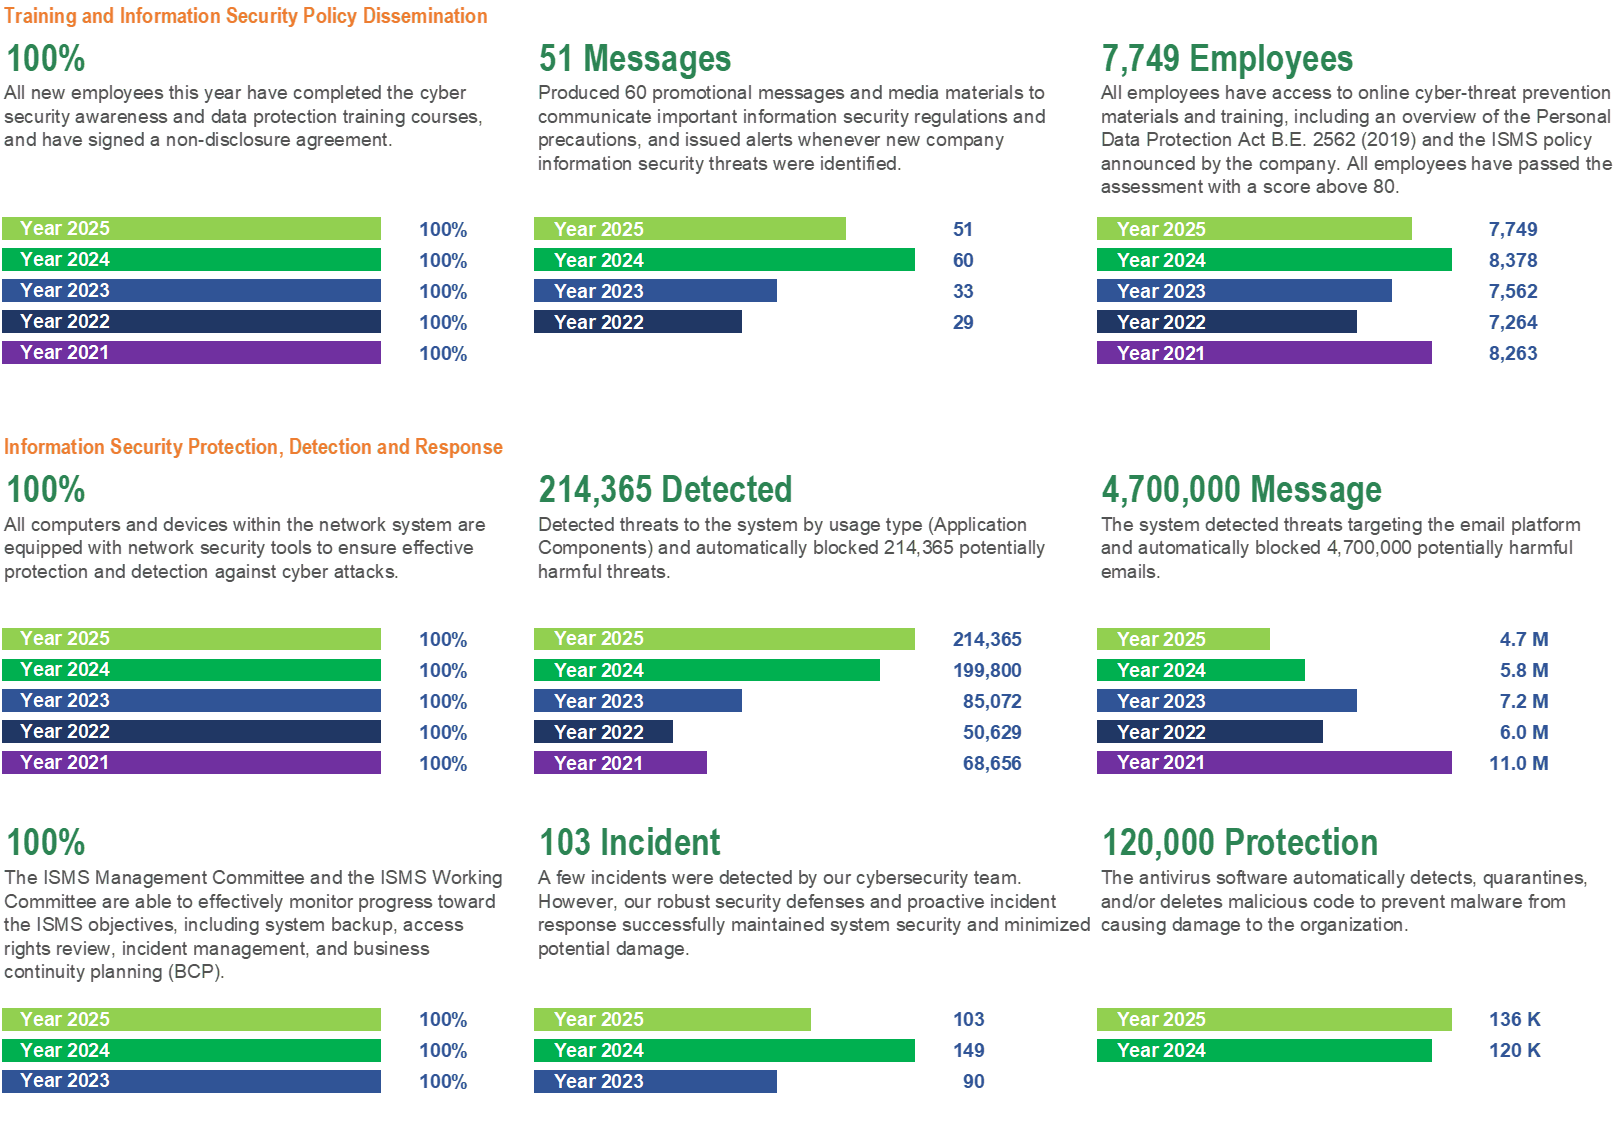
Completion rate of new employee information security training and NDA signing100%100%100%100%
Information security communication messages and media materials (items)29336051
Employees with access to online information security materials (persons)7,2647,5628,3787,749
Note: All employees have access to online cyber-threat prevention materials and training, including the Personal Data Protection Act and the ISMS policy announced by the Company, and all employees scored 80 points or above in the assessment. Employee numbers are based on the headcount as of November 30, 2025.
6. Information Security Protection, Detection and Response
Item 2022 2023 2024 2025
Networked computers and devices equipped with security tools100%100%100%100%
System threats automatically blocked (times)50,62985,072199,800214,365
Harmful emails automatically blocked (messages)6.0 M7.2 M5.8 M4.7 M
ISMS objective monitoring achievement rate100%100%100%
Information security incidents detected (times)90149103
Malicious code detected, quarantined or deleted by anti-virus software (times)136,000120,000
Note: Items monitored by the ISMS Management Committee and the ISMS Working Committee include system backup, access rights review, incident management and business continuity planning (BCP). All information security incidents detected by the cybersecurity team were effectively contained through existing defenses and proactive incident response, minimizing potential damage.
7. Reporting Channel
TEL: (02) 2717-0032
E-mail: ethics@apex-intl.com.tw